WMS security and recovery: questions for your vendor and team
Assign access, incident, backup, and recovery responsibilities for warehouse software using an evidence-focused security review.
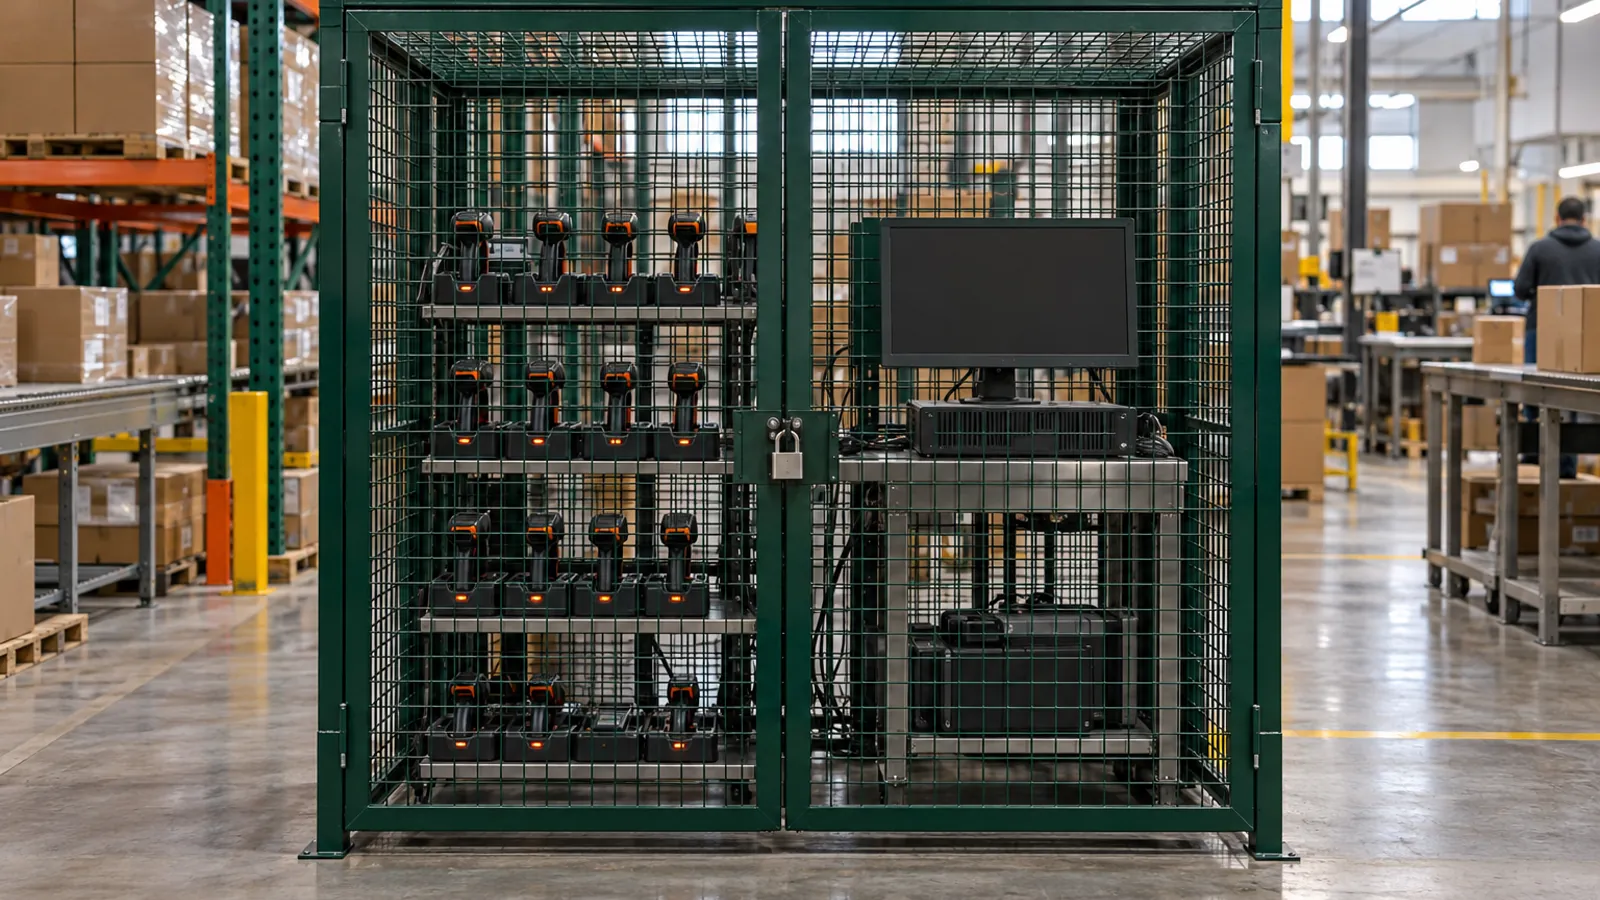
A WMS security review should establish who can access warehouse data, change critical states, support the service, and restore a consistent operation after disruption. Ask for evidence and responsibilities rather than a general assurance that the system is secure. Use the FTC and NIST resources as guidance for your review; they do not certify an individual product or remove your obligations under contracts and applicable law.
Map the assets and access paths
List the application, interfaces, identity provider, handhelds, printers, local computers, network equipment, exports, and support accounts. Identify the information each holds, including customer addresses or employee data where present. Keep only the data needed for the task. A warehouse application can expose information through exports and integrations even when the main screen appears tightly restricted.
Assign an owner to access approval, role changes, offboarding, and emergency access. Review supplier and contractor access as well as employees. Confirm authentication controls, including multifactor authentication for appropriate sensitive access, against the actual proposed service. Do not assume an advertised feature is enabled in your tenant or available in the edition being purchased.
Test roles through meaningful actions
| Action | Review question |
|---|---|
| Stock adjustment | Who can create and approve it? |
| Hold release | Is authority restricted appropriately? |
| Data export | Who can retrieve sensitive records? |
| Interface change | Who can alter mappings or credentials? |
| User administration | Can access be removed promptly? |
| Support access | Is it approved, limited, and recorded? |
Use separate test accounts representing real roles. Try both permitted and prohibited actions, including through APIs or alternate screens where relevant. Record the outcome and any audit evidence. Avoid relying only on a role name such as operator or supervisor; the effective permissions are what determine the control. Retest after meaningful configuration or identity changes.
Define backup and recovery scope
Ask what data and configuration are backed up, how often, how long copies are retained, and who can restore them. Include custom mappings, documents, and local components if they are necessary to operate. Agree on acceptable data loss and restoration targets with the business and service owners. A statement that backups exist does not establish that a warehouse can recover within its needs.
Request evidence of a controlled restoration exercise. Verify that restored data can support transactions and that stock, open orders, and interface queues are reconciled. An application database and integration queue restored to different moments may require investigation. Define the coordinator who brings suppliers and internal teams together rather than leaving recovery as several disconnected technical tasks.
Prepare an incident procedure
Give staff a clear route to report suspicious access, lost equipment, unexpected exports, or service disruption. Identify who can disable access, isolate a device, pause an interface, and communicate with affected parties. Preserve relevant evidence without exposing secrets or unnecessary personal information in general chat channels. Legal and security advisers should determine any notification obligations for the actual event.
Run an illustrative tabletop exercise: an administrator account is unavailable and shipment confirmations are delayed during a busy shift. Ask how the warehouse distinguishes a service failure from a security event, who authorizes continued work, and how later reconciliation is performed. The point is to discover missing contacts and decisions before the event, not to claim that a meeting proves readiness.
Keep the review current
Review access, device inventory, support accounts, recovery evidence, and vendor responsibilities after relevant changes. Rotate or revoke credentials under an approved process and test the interfaces afterward. Keep secure records of contacts and procedures accessible during an outage. A plan stored only inside the unavailable application may be difficult to use when it is needed.
Confirm product-specific and jurisdiction-specific obligations with qualified professionals. This guide does not decide whether a privacy law, sector rule, or customer security clause applies to you. Request current supplier documentation and independent evidence where appropriate, then assess its scope and limitations. A report covering one service or period should not be treated as a blanket guarantee for every integration and operating practice.
FAQ
Does a cloud supplier handle all security?
No general assumption is safe. The supplier and customer have specific responsibilities for access, devices, data, configuration, and interfaces. Record the division for the proposed service.
Is an export a backup?
It can preserve some information, but may omit configuration, relationships, history, or files required for recovery. Test whether the available materials can restore the needed operation.
Can the warehouse keep shipping during an incident?
Only under an approved continuity process that preserves safety, authorization, and transaction reconciliation. Define who can make that decision before an incident occurs.
Continue your decision
- WMS operating risks: a practical control map — Map warehouse failure paths to inventory controls, owners, detection signals, and recovery evidence before the next exception.
- Cycle counting in a WMS: investigate before adjusting — Design a count process with movement controls, independent recounts, variance investigation, and an auditable adjustment decision.
- Lot and serial tracking: test traceability through exceptions — Define lot and serial events across receipts, movements, holds, returns, and shipments, and verify requirements with official sources.
- Use the launch readiness checklist to connect this guide to a practical planning task.
- Compare WMS approaches before treating a product category as a complete specification.
Sources and scope
Official pages checked on October 30, 2026. The planning procedures, test scenarios, and worked examples are original editorial guidance, not prescribed standards or evidence of product testing.
- FTC — Cybersecurity for Small Business — General business security practices and vendor-risk questions.
- NIST — Cybersecurity Framework 2.0 for Small Business — Voluntary risk-management guidance; not a product certification.